Español
 Português (Brasil)
 Français
 Deutsch
 Italiano
 Nederlands
 Polski
 Svenska
 Türkçe
 Русский
 日本語
 한국어
 简体中文
 Tiếng Việt
 Bahasa Indonesia
 繁體中文
 Čeština
 Dansk
 Norsk (bokmål)
 Suomi
 Ελληνικά
 Română
 Magyar
 Українська
 ไทย
 हिन्दी
 العربية
 עברית
What Is a Third-Party Cookie?
A third-party cookie is a small piece of data stored by a domain other than the one a user is currently visiting, used to track behavior across sites.

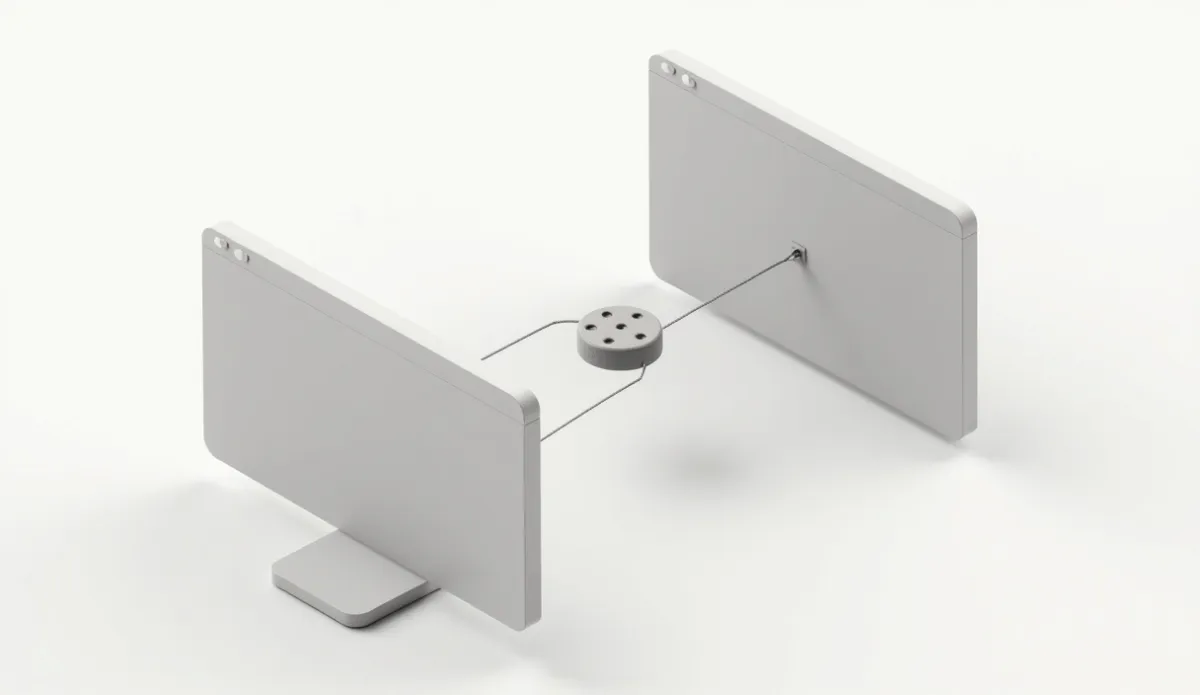
A third-party cookie is a small piece of data stored by a domain other than the one a user is currently visiting, most often placed by an ad tech company's tracking script embedded on a publisher's page. Because the same ad tech domain can be embedded across thousands of unrelated sites, its cookie lets that company recognize the same browser across all of them, which is what made third-party cookies the backbone of cross-site ad targeting and frequency capping for most of the last two decades.
First-party vs third-party, in plain terms#
| Type | Set by | Typical use |
|---|---|---|
| First-party cookie | The domain the user is actually visiting | Login sessions, cart contents, site preferences |
| Third-party cookie | A different domain, embedded via script or pixel | Cross-site ad targeting, retargeting, frequency capping |
First-party data is collected directly by a business about its own users and doesn't depend on this cross-site cookie mechanism at all, which is exactly why it's become more valuable as third-party cookies get restricted.
Why browsers moved away from them#
Safari and Firefox blocked third-party cookies by default years ago. Chrome, which carries the largest browser market share, has moved through multiple phases of restricting and deprecating them as part of a broader browser-level privacy initiative built around new targeting and measurement APIs. The underlying concern regulators and browser makers raised was the same one shaping Real-Time Bidding privacy rules generally: a user's browsing behavior across unrelated sites was being stitched together without clear consent. That same initiative also touches OpenRTB implementations, since bid requests historically carried cookie-based identifiers that the new APIs are designed to avoid.
What this means for native and programmatic targeting#
Cross-site behavioral targeting and frequency capping that depended on third-party cookies work less reliably as browsers restrict them, pushing the industry toward contextual targeting, matching ads to page content rather than user history, authenticated first-party identifiers, and cohort-based approaches proposed under the Privacy Sandbox umbrella. A Data Management Platform built primarily around cross-site cookie data has had to adapt the same way. Native advertising was already less dependent on cross-site retargeting than open-web display, since native inventory is usually bought contextually within a publisher's own content feed rather than chased across the web, so the practical impact on native buying has generally been smaller than on retargeting-heavy display and social prospecting.
What advertisers are doing instead#
- Building first-party data directly through email capture, logged-in experiences, and loyalty programs.
- Leaning more on contextual targeting for prospecting, which doesn't require tracking a user across sites at all.
- Working with publishers' own authenticated ID solutions where available.
- Testing Privacy Sandbox APIs as Chrome's rollout progresses, checking current documentation since the timeline and mechanics have shifted more than once.
This shift touches programmatic advertising generally, not just retargeting, since header bidding auctions and real-time bidding both leaned on the same cross-site cookie plumbing for years.
How OpenAdLibrary helps#
Contextual, feed-based native placements were never as dependent on third-party cookies as retargeting-heavy display campaigns, one reason some advertisers have shifted budget toward native as cookie-based targeting gets less reliable elsewhere. OpenAdLibrary's native ad spy tool can show how advertisers in your vertical are already running contextual-first native creative.